Leading the Curve of Innovation: Dr. Jones and his physician associates have pioneered research that lead directly to U.S. market approval of today's most popular injectables including Botox®, Voluma®, Juvéderm®, Kybella®, Belotero®, and many more.
Fortify Default Accounts and Administrative Access Controls
Every system has a story: attackers often start by probing default usernames and passwords, treating them like unlocked doors. Treat initial accounts as fragile evidence; if a login behaves oddly it's a Red Flag; respond quickly and isolate the account.
Hardening means more than new passwords. Replace generic admin IDs with named accounts, enforce unique strong credentials, and remove or rename hard-coded service users. Keep a secure, auditable backup of credentials off-device (a Hard Copy is useful for emergency recovery) and require regular credential rotations.
| Action | Purpose |
|---|---|
| Rename/Disable | Reduce default access |
| Audit | Detect misuse |
Operational controls matter: restrict admin access by source IP, use tiered admin roles, enable session timeouts, and Verify MFA enrollment for every privileged user. Combine these controls with frequent audits and incident drills to close common attack paths. Document changes and communicate them to your team.
Enable Two-factor Authentication Across All User Logins
As teams log in from home and cafes, a simple password no longer suffices; weaving a second factor into every access path transforms risk into manageable control. For azeetop administrators, framing the change as part of user safety — like counseling a patient about an Rx — makes adoption conversational rather than punitive. Choose standards-based methods (TOTP apps, hardware keys, FIDO2) and enforce enrollment during onboarding so accounts never remain single-factor.
Complement technical controls with clear Sig-style guidance, automated resets for lost second factors, and monitoring that flags anomalies as Red Flag events. Integrate 2FA into VPNs, admin consoles, and remote desktop gateways, and test recovery workflows regularly. Balance security with usability: offer backup options and periodic drills so teams treat multi-factor access as routine, not a barrier. Document exceptions and train staff on phishing recognition and safe device habits.
Harden Network Settings and Secure Remote Connections
When I first joined an operations team, nights meant chasing suspicious logins and treating every anomalous connection as a Red Flag. Our early azeetop deployments taught us to lock down ports, enforce strong ciphers, and segment services, shrinking the blast radius for inevitable compromises. Avoid trusting defaults now.
Remote access demanded strict controls: zero trust tunnels, multi factor verification and ephemeral credentials. We rotated keys, pinned certificates and used bastion hosts carefully. Audit rules logged every session and tools automatically Verify device posture before granting access, reducing attacker dwell time and human error.
Operationally, enforce least privilege for maintenance, disable legacy protocols like Telnet and older TLS, and change default ports for admin interfaces. Combine IP allowlists, jump hosts, and continuous IDS and IPS monitoring to catch intrusion patterns early; then document changes in a Hard Copy change log for compliance and audits.
Implement Role-based Permissions and Least Privilege Policies
On azeetop systems, begin by mapping job functions and responsibilities so access is tightly aligned to real needs. Define clear roles and enforce separation of duties for safer operations today.
Grant only the minimum privileges needed and use temporary elevation for special tasks; require approval workflows and reviews. Watch for a Red Flag pattern in entitlement changes and anomalous access.
Schedule periodic role recertification, automatic reviews, and tight onboarding/offboarding processes. Use tools to simulate privileges and reduce blast radius. Avoid hidden Golden Handcuffs that mask excessive access accumulation over time.
Keep Firmware Updated and Monitor Security Notifications
In an azeetop deployment, a midnight operator skipped a routine check and woke to cascading failures. That narrative shows why scheduled maintenance windows, clear ownership, and a tight inventory matter; treating vendor bulletins as a Red Flag reduces surprise and speeds recovery.
Automated verification, staging, and safe rollback lessen risk. Subscribe to vendor feeds, enable alerts Stat, and run integrity checks frequently. Keep change logs concise with Sig for each device, maintain test benches, and rehearse restores so teams can respond quickly to incidents. Document timelines and owners; verify backups.
| Alert | Action |
|---|---|
| Update | Notify |
Audit Logs Regularly and Respond to Incidents Quickly
When a midnight alert flashes, the team gathers like pharmacists responding to an urgent call. Logs tell the story of what happened, when, and who — essential evidence to reconstruct attacks and stop spreading damage fast.
Make log retention policies practical: set collection, centralization, and tamper-proof storage so investigators can work Stat and without losing critical context. Normalize time stamps, correlate events, and retain enough history to spot slow-moving intrusions too.
Design clear Sig for escalation: alerts should carry priority, affected assets, initial indicators, and recommended containment steps. Training tabletop exercises builds reflexes so responders act swiftly, reducing dwell time and business impact and reputational harm.
Automate initial triage but preserve human oversight; playbooks accelerate containment while analysts validate root cause. Treat anomalies as Red Flag events, verify suspicious behavior, and follow escalation matrices so recovery can begin within minutes today.
If you are ready to schedule a consultation with Dr. Jones for the treatment of your choice, you can request a consultation with us online or call our office at 310.246.0495 for more information.

See the advanced approaches our Skin Care and Laser Physicians of Beverly Hills team uses to help you Relax, Refill, Resurface, and Reduce. Explore the contributions of Dr. Derek Jones and his team in making some of the most sought-after treatments accessible to the public.
Get "inside" information on a wide range of treatments and procedures available at our practice on our regularly updated blog. We also provide tips and advice for maximizing and prolonging your results to maximize skin health and beauty.
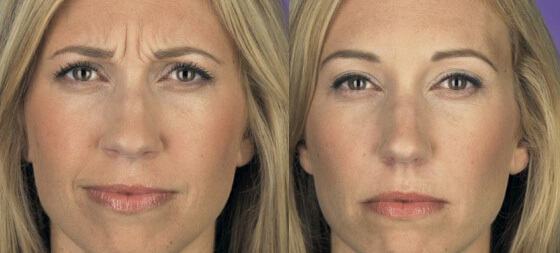 *Patient results may vary.
Our photo gallery shows the results that injectables, lasers and light-based treatments, and other cosmetic options can provide. From reducing fat and smoothing wrinkles to minimizing scars from skin cancer removal, take a look at what we can do to help.
As an aesthetic and surgical dermatologist trained in Mohs micrographic surgery for skin cancer removal, Dr. Naissan Wesley is a highly sought-after source on the subject of skin. Read her articles and see who's talking about her on her media page.
SKIN CARE & LASER PHYSICIANS OF BEVERLY HILLS - 9201 W. Sunset Blvd. Suite 602, Los Angeles, CA 90069 US 310.246.0495
Stay up to date on the Skin Care & Laser Physicians of Beverly Hills happenings by following us on Facebook, Twitter, Instagram, and more.
Copyright 2022 Dr. Derek Jones Skin Care and Laser
Dr. Derek H. Jones heads Skin Care and Laser Physicians of Beverly Hills, offering aesthetic dermatology, including BOTOX®, Juvéderm®, Kybella™, laser skin resurfacing, and CoolSculpting®, as well as surgical and medical dermatology, including skin cancer, acne, and rosacea treatments, to Los Angeles, Beverly Hills, West Hollywood, and beyond.
 Videos
 Gallery
 Media